 BTC
 ETH
 SOL
 XRP
 BNB
 DOGE
 ADA
 AVAX
 LINK
 TON
 DOT
 LTC
 TRX
 POL
 USDT
 USDC
 SUI
 HBAR
 SHIB
 BCH
 XLM
 NEAR
 APT
 ARB
Bitcoin Core fixes AI-found flaw that could stall nodes
Bitcoin Core disclosed a medium-severity bug, found with AI-assisted research, that let malicious peers freeze nodes for over 12 seconds per message. Patched releases are out for most branches.
Why it matters: The disclosure shows AI tools are finding bugs in Bitcoin's core software faster, and that node operators must patch promptly to avoid temporary disruption.
Key points
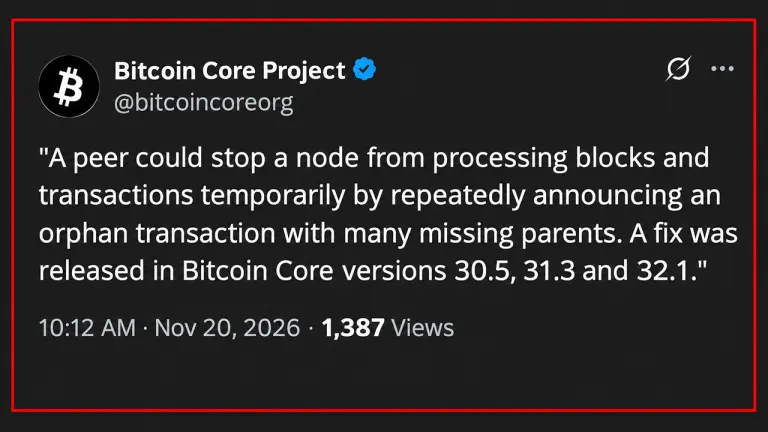
- The flaw, CVE-2026-117348, affected Bitcoin Core versions 29.0-29.5, 30.0-30.4 and 31.0-31.2; fixes are in 30.5, 31.3 and 32.1.
- Project Loupe, an LLM security initiative run by Elias Rohrer at Spiral, reported the bug on 8 July 2026; the fix was merged on 6 Aug.
- The discontinued 29.x branch will get no further patches, Bitcoin Core said in its 20 Nov 2026 disclosure.
Bitcoin Core has disclosed a medium-severity flaw that could let malicious peers temporarily stall nodes, after the bug was found through AI-assisted security research. The project published the advisory on 20 Nov 2026, cataloguing the issue as CVE-2026-117348 and describing it as a node stall through duplicate orphan announcements.
The bug lay in how the software handled its holding area for transactions awaiting missing parent transactions. Inventory messages can carry 50,000 entries, and the software did not ignore repeated announcements of the same orphan. An attacker could therefore force a node to repeat costly checks thousands of times, stalling it for more than 12 seconds per message.
Versions 29.0 to 29.5, 30.0 to 30.4 and 31.0 to 31.2 were affected.
Project Loupe, an automated large language model security initiative run by Elias Rohrer at Spiral, Block's open-source Bitcoin development division, reported the flaw on 8 July. Bitcoin Core developer Gregory Sanders validated it, and the fix was merged on 6 Aug before reaching Bitcoin Core 32.1 on 27 Oct. The advisory set out no way to steal Bitcoin or permanently damage nodes. Bitcoin Core changed its disclosure policy in October to speed up publication of easily discoverable issues.
What to watch: Node operators on affected branches are expected to upgrade to versions 30.5, 31.3 or 32.1, with no patches planned for the discontinued 29.x branch.
Live updates on NewsFeeds:BitcoinAIFrom our AI Hub: Is ChatGPT, Claude or Gemini down?, AI API prices, new AI modelsDesk editor: Keshav Aggarwal (accountable for this page; this summary was not edited by hand)
How this was produced: an AI model wrote this summary of Bitcoin.com News’s report, which we credit and link above. Read our Editorial and AI policy. Spotted a mistake? See Corrections.
Not investment advice. Read the risk disclaimer.