 BTC
 ETH
 SOL
 XRP
 BNB
 TON
 DOT
 LTC
 POL
 HBAR
 NEAR
 ARB
 UNI
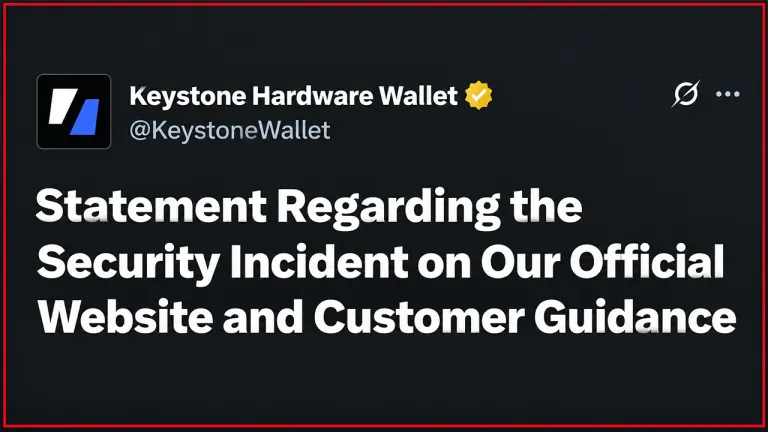
Keystone says stolen authentication key forces destruction of 18,835 wallets
Hardware wallet maker Keystone will scrap 18,835 devices after attackers obtained the key used to verify its products are genuine, and says 25,964 buyer records kept personal data.
Key points
- Keystone disclosed on 26 Oct 2026 that attackers stole the WebAuth key used to authenticate its hardware wallets.
- All 18,835 devices in existing inventory will be destroyed; new wallets get a replacement key.
The manufacturer traced the intrusion to a flaw in a third-party data monitoring tool that let attackers escalate their access. Keystone spotted suspicious activity on 20 Oct, disabled the affected website functions and began a forensic investigation.
An attacker holding it could build counterfeit devices that pass Keystone's authenticity checks, potentially exposing buyers to asset theft. Keystone plans to destroy all 18,835 units in stock and give newly made wallets a replacement key. Shipments of outstanding website orders are suspended, with preorders taken until replacement production is ready.
Keystone said its automated deletion system had malfunctioned, leaving data stored beyond its 180-day retention policy.
Devices delivered before 20 Oct remain safe if they pass authentication, while later ones using the compromised key need extra checks through customer support.
What to watch: Keystone expects overdue buyer data deletion requests submitted on 24 Oct to be finalised by 3 Nov, and plans breach lookup tools and further security audits.
Live updates on NewsFeeds:AltcoinsDesk editor: Keshav Aggarwal (accountable for this page; this summary was not edited by hand)
How this was produced: an AI model wrote this summary of Bitcoin.com News’s report, which we credit and link above. Read our Editorial and AI policy. Spotted a mistake? See Corrections.
Not investment advice. Read the risk disclaimer.