 BTC
 ETH
 SOL
 XRP
 BNB
 TON
 DOT
 LTC
 POL
 HBAR
 NEAR
 ARB
 UNI
Keystone says website breach exposed buyers' shipping data
The hardware wallet maker says an unauthorised party obtained customer names, contact details and purchase information through its website, while private keys and recovery phrases stayed secure.
Why it matters: Hardware wallets keep keys offline, but this breach shows customer identities and addresses can still be exposed, feeding the phishing and impersonation scams that target crypto holders.
Key points
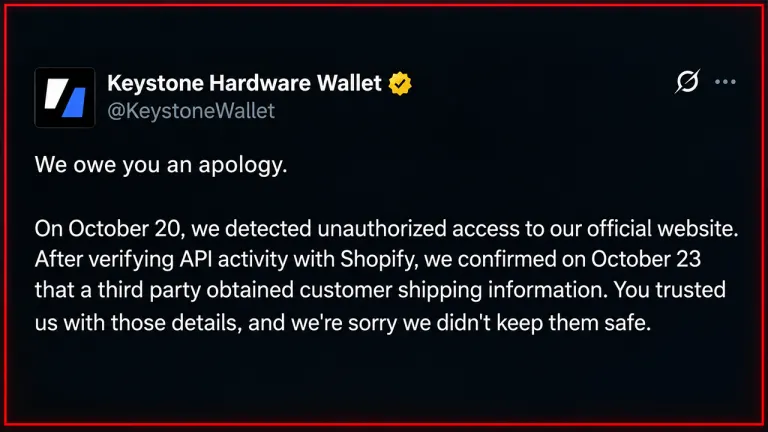
- Keystone detected suspicious access on 20 Oct and confirmed the unauthorised access by 23 Oct, disclosing it on 24 Oct.
- Names, contact information, shipping addresses and purchase details were exposed; payment information was not.
- Keystone warned of fake refund offers and replacement devices, and says it never asks for recovery phrases or private keys.
Keystone has disclosed a customer data breach at its online storefront, saying an unauthorised party obtained buyers' shipping information and purchase details.
According to the company, it spotted suspicious access on 20 Oct and reviewed application programming interface activity with Shopify, its e-commerce provider. By 23 Oct it had confirmed that names, contact information, shipping addresses and purchase details had been taken.
The immediate risk is impersonation rather than drained wallets. One X user, OG Degen, wrote the day before the disclosure that a caller from a spoofed Montreal number had tried to social-engineer them.
The incident adds to a difficult year for hardware wallet makers.
What to watch: Keystone says it has begun notifying affected customers, though it has not said how many buyers were exposed.
Live updates on NewsFeeds:AltcoinsDesk editor: Keshav Aggarwal (accountable for this page; this summary was not edited by hand)
How this was produced: an AI model wrote this summary of Bitcoin.com News’s report, which we credit and link above. Read our Editorial and AI policy. Spotted a mistake? See Corrections.
Not investment advice. Read the risk disclaimer.