Fake Giwa L2 chain drains 766 ETH from 1,335 users
Scammers built a working fake Ethereum layer-2 chain impersonating Upbit-backed Giwa, draining over $2m from users who bridged funds. DYORSWAP, which flagged the chain, is refunding victims but faces criticism.
Key points
- About 766.25 ETH, worth more than $2 million, was drained from roughly 1,335 addresses that bridged funds to the fake chain.
- The chain used Chain ID 9134 and was first identified by DYORSWAP, a multichain decentralised exchange, as the Giwa mainnet.
- DYORSWAP said the deployment included OP stack-style infrastructure, a bridge and a batcher, showing unusual sophistication.
- Giwa said it had not stealth-launched its mainnet and that posts claiming to have its mainnet RPC details were untrue.
- DYORSWAP has begun reimbursing users and says it has already distributed over 200 ETH from its own funds.
A fake Giwa layer-2 chain drained 766.25 ETH, worth more than $2 million, from about 1,335 users who bridged funds to it, Bitcoin.com News reports. The chain, which used 9134 as its Chain ID, was first identified by DYORSWAP, a multichain decentralised exchange, as the mainnet of Giwa, a project backed by Upbit.
According to the report, the fake Giwa L2 chain was presented to early adopters as a chance to bridge funds quickly and capture financial opportunities. DYORSWAP initially treated the deployment as genuine, and user activity on the chain included buys, sells and token launches happening in real time before the funds were taken.
Fake chain drains 766 ETH
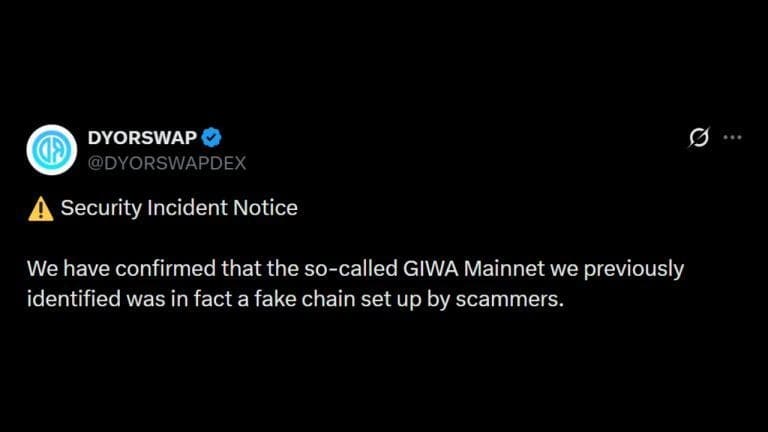
Some observers initially claimed the scheme simply involved taking an ordinary Ethereum address and presenting it as an L2 chain. In its official report, DYORSWAP rejected that description, saying the deployment included OP stack-style infrastructure, a bridge and a batcher, which pointed to a higher level of sophistication.
Once DYORSWAP detected that user funds had been drained, it warned people not to use any unofficial Giwa mainnet RPC, bridge or contract, and not to send funds to related addresses. The real Giwa project also clarified that it had not stealth-launched its mainnet, stating that posts claiming to hold Giwa mainnet RPC information were not true.
Sophisticated deployment
DYORSWAP denied direct responsibility for the attack, saying the funds were taken from the fake chain, and began a reimbursement process for affected users. It said it had already distributed more than 200 ETH from its own funds and would keep investigating, reconstructing the fake chain's transaction history to identify and trace the attacker's addresses.
Even so, users criticised DYORSWAP's role, arguing that without its involvement nobody would have noticed the chain launch or bridged funds onto it, and describing the episode as a social engineering scam. The incident follows a series of security breaches affecting both decentralised and centralised platforms, which Bitcoin.com News says are keeping crypto holders on constant alert.