 BTC
 ETH
 SOL
 XRP
 BNB
 TON
 DOT
 LTC
 POL
 HBAR
 NEAR
 ARB
 UNI
Electrum says malicious servers hid Bitcoin theft behind fee bumps
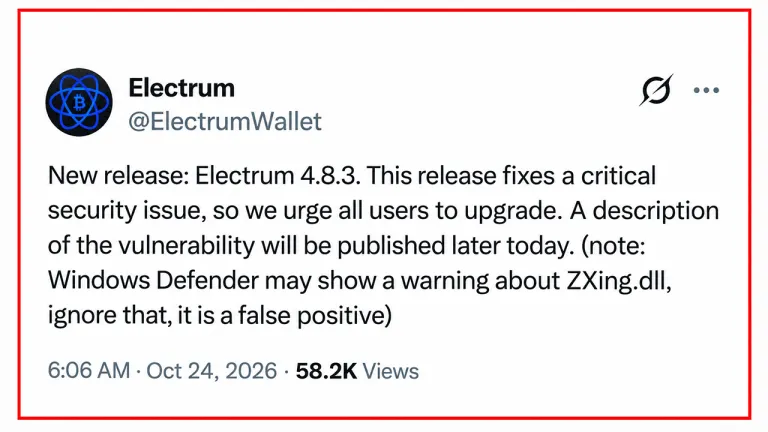
Electrum has released version 4.8.3 to fix a high-severity flaw that let malicious servers swap a user's payment for a thief's transaction, with one user losing funds after approving a fee increase.
Why it matters: The flaw let a wallet built to protect private keys be manipulated into signing a payment its owner never intended, and attackers had already stolen funds with it.
Key points
- Electrum 4.8.3, released on 24 October, patches a flaw affecting every earlier version, documented in advisory GHSA-6jp4-8v48-cc5v.
- A compromised server could block a legitimate payment and substitute a fraudulent one to an attacker's address, with matching final four characters.
- Users dannydeezy and Raju-K12 reported the issue privately on 11 Oct and 18 Oct, the second after losing funds.
Electrum has released version 4.8.3 to close a high-severity flaw that let malicious servers substitute transactions, warning users to upgrade immediately. The wallet's developers said every earlier version was affected and that attackers had already used the loophole to steal funds, Bitcoin.com News reports.
Older versions checked confirmed transactions themselves but accepted some unconfirmed ones without verifying signatures. A compromised server could hold back a genuine payment and put a fraudulent one in its place, which Electrum showed as an ordinary pending payment.
The trap sprang when users tried to raise fees through Replace-By-Fee. Instead of lifting the fee on their own payment, victims could sign the substituted transaction and send their Bitcoin to the attacker. Attackers also generated addresses whose last four characters matched the intended destination, and one fraudulent transaction carried a zero fee, apparently to prompt the fee change.
Developers received two private reports. On 11 Oct, user dannydeezy reported transaction substitution, though the fee mechanism was not fully understood. The patch, commit 90fe308, makes Electrum verify signatures on unconfirmed transactions spending the wallet's coins and reject invalid ones. Users should download only from electrum.org and check destination addresses before signing.
What to watch: Users on versions earlier than 4.8.3 are urged to upgrade from electrum.org and verify the download's cryptographic signatures.
Live updates on NewsFeeds:BitcoinDesk editor: Keshav Aggarwal (accountable for this page; this summary was not edited by hand)
How this was produced: an AI model wrote this summary of Bitcoin.com News’s report, which we credit and link above. Read our Editorial and AI policy. Spotted a mistake? See Corrections.
Not investment advice. Read the risk disclaimer.